Tiny 2FA + Brute Force Protection
by Web Guy 0 (0 reviews)

Tiny 2FA + Brute Force Protection

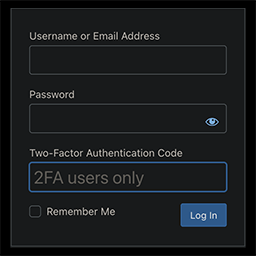
A simple two-factor authentication plugin that just works.

Tiny 2FA + Brute Force Protection ranks #26,910 among WordPress.org plugins with 20+ active installations, is #575 of 1,584 in the Authentication category, and was last updated Jun 4, 2026. Data from WordPress.org, refreshed twice daily — see methodology.

Tested up to WP 7.0.5 (Current: 7.1)
v0.4 Current Version v0.4
Updated 3 months ago Last Update on 04 Jun, 2026
Refreshed 11 hours ago Last Refreshed on
#575 of 1,584 in Authentication Top 50% by installs
View on WordPress.org
Rank
#26,910
No change
Active Installs
20+
-20%
KW Avg Position
43.5
1 worse
Downloads
925
+2 today
Support Resolved
0%
No change
Rating
0%
Review 0 out of 5
0 (0 reviews)

Next Milestone 30

Total Progress 70%
20+ 30+
4,697
Ranks to Climb
-
Growth Needed
8,000,000
Active Installs
Pro

Unlock Exact Install Count

See the precise estimated active installs for this plugin, calculated from real-time ranking data.

  • Exact install estimates within tiers
  • Track install growth over time
  • Milestone progress predictions
Upgrade to Pro
Need 3 more installs to reach 30+

Rank Changes

26,656 26,745 26,834 26,923 27,012 11-09-2026 12-09-2026 13-09-2026 14-09-2026 15-09-2026 16-09-2026 17-09-2026 18-09-2026
26,508 26,681 26,854 27,027 27,200 03-09-2026 04-09-2026 05-09-2026 06-09-2026 07-09-2026 08-09-2026 09-09-2026 10-09-2026 11-09-2026 12-09-2026 13-09-2026 14-09-2026 15-09-2026 16-09-2026 17-09-2026 18-09-2026
Current #26,910
Change
Best #

Upgrade to Pro

Unlock 30-day and 90-day rank history charts with a Pro subscription.

Upgrade Now

Active Installs Growth

Active Installs 0,000,000+
Growth +0.0%
Peak 0,000,000

Downloads Growth

0 10 11-09-2026 12-09-2026 13-09-2026 14-09-2026 15-09-2026 16-09-2026 17-09-2026 18-09-2026
0 10 03-09-2026 04-09-2026 05-09-2026 06-09-2026 07-09-2026 08-09-2026 09-09-2026 10-09-2026 11-09-2026 12-09-2026 13-09-2026 14-09-2026 15-09-2026 16-09-2026 17-09-2026 18-09-2026
Downloads
Growth
Peak

Upgrade to Pro

Unlock 30-day, 90-day, and yearly download history charts with a Pro subscription.

Upgrade Now

Reviews & Ratings

0.0
0 reviews
Overall 0%
5
0 (0%)
4
0 (0%)
3
0 (0%)
2
0 (0%)
1
0 (0%)

Frequently Asked Questions

Common questions about Tiny 2FA + Brute Force Protection
Only TOTP at this time. This is the most common 2FA method, the one you're probably most familiar with already. It's more secure than 2FA via SMS or email, but not as secure as a hardware key (overkill for most people), which is probably the only other option I'd consider adding.
There are many mobile, desktop, and browser apps that support TOTP, including: Google Authenticator, Microsoft Authenticator, Proton Authenticator, Ente Auth, Authy, Bitwarden, LastPass, and 1Password.
Simply regenerate (↻) in your profile settings to get a new key.
Yes. For extra security, you can define your encryption key in wp-config.php: define( 'TINY_2FA_ENCRYPTION_KEY', 'your-64-character-hex-key-here' ); You can find your current key in /wp-content/tiny-2fa-backup.php. This ensures your key survives database issues if somehow it's lost.
Other than storing secret keys in an encrypted format (apparently most sites just save them in plaintext), it's a pretty standard implementation (but having any 2FA in place is infinitely more secure than no 2FA at all).
As it turns out, generating QR codes is not a trivial matter. I explored generating them locally, but it added a lot of bloat to the plugin. So, I've opted to use an external service instead. I'm using QuickChart (rather than Google, a popular choice) to generate QR codes, and for extra privacy, proxying the requests through Cloudflare. QuickChart will only ever know the secret key, but not the site name, username, or IP address it belongs to. Cloudflare will know the server IP the request is coming from, but still not the name of the website or user.
The way I've envisioned Backup Codes is simple: immediately upon enabling 2FA, Backup Codes will be on by default. This means that you'll receive codes by email until you're certain you've set up an authentication app correctly, and then you should disable them.
I don't like the current implementation of the common Backup Codes feature that comes with most 2FAs. I think it creates a burden for the user to back them up, which if they're capable of doing, they're also capable of backing up their secret key in the first place without adding an unnecessary chore and new vulnerability while they're at it. I think I've been able to improve upon the concept of Backup Codes, at least in the WordPress environment where most users are going to be the admin of their own website anyway. The entire point of Backup Codes in the first place is to offer a second chance to avoid being locked out of your account in case you lost your secret key. But for most WordPress websites, and probably many websites in general these days, the added vulnerability doesn't seem to match the intended usefulness. I'm open to being wrong about this. If you feel my thinking is flawed or you have any other suggestion for improving the security of Tiny 2FA, please let me know.

More plugins by Web Guy

Sign In / Register

You need to sign in or register to use this feature.